Turn local security scans into FDA-submission-focused evidence.
Anzen helps medtech regulatory and software teams produce FDA-submission-focused SAST and SBOM reports. Scans run on your own machines and CI runners, and code snippets can be stripped before results leave your network.
Security evidence built from the workflow teams already use.
Built for medtech and regulated software teams that need practical developer feedback and credible evidence for medical device submissions and design records.
Scan code and SBOMs where they live
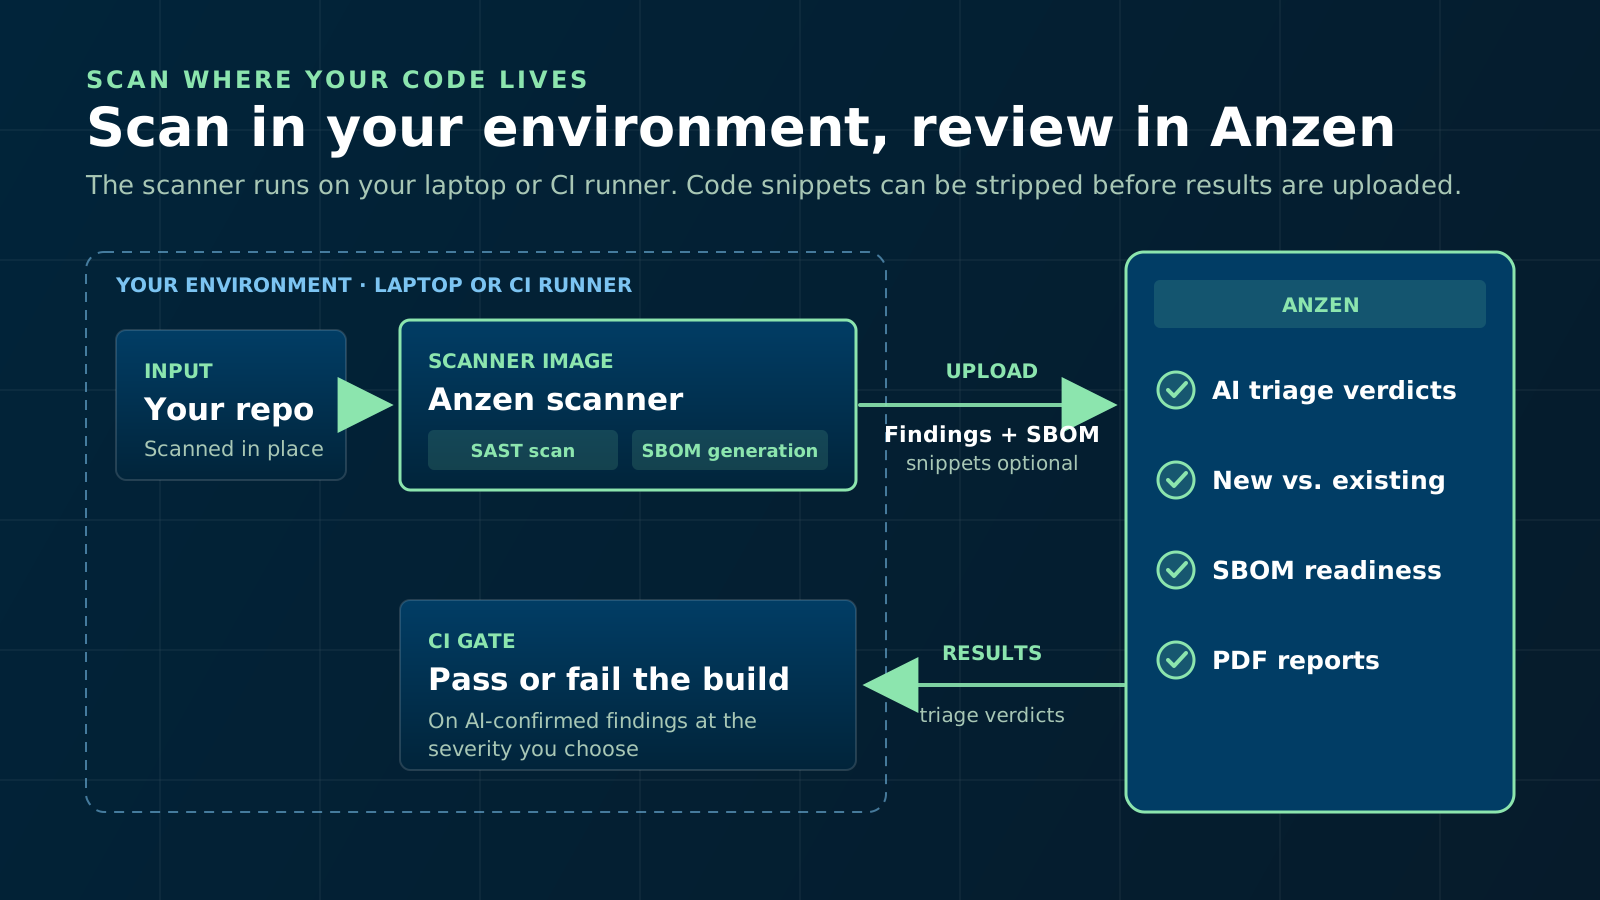
Run the Anzen scanner image on a laptop, in GitHub Actions, or in GitLab CI. It runs a SAST scan, generates a CycloneDX SBOM, and can strip code snippets before anything is uploaded. SARIF from scanners you already run can be uploaded too.
Prioritize SAST findings with AI-assisted triage
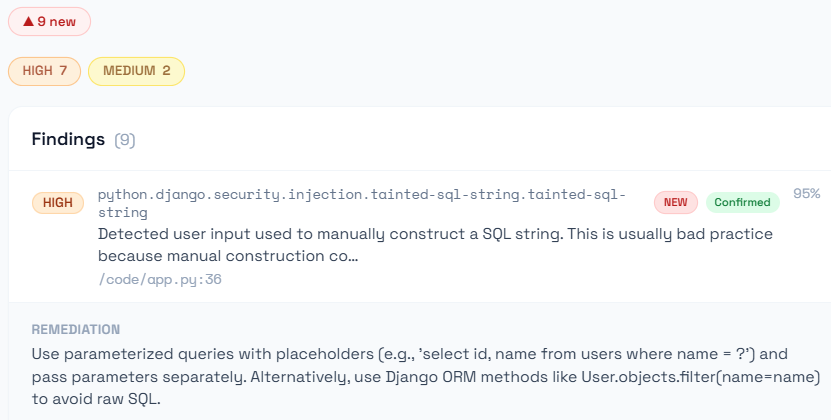
AI triage gives findings an advisory verdict with a confidence score, remediation guidance, and a suggested FDA premarket security control category. Your team records dispositions with written justifications, and they carry into later scans.
Review SBOM readiness against NTIA and FDA expectations
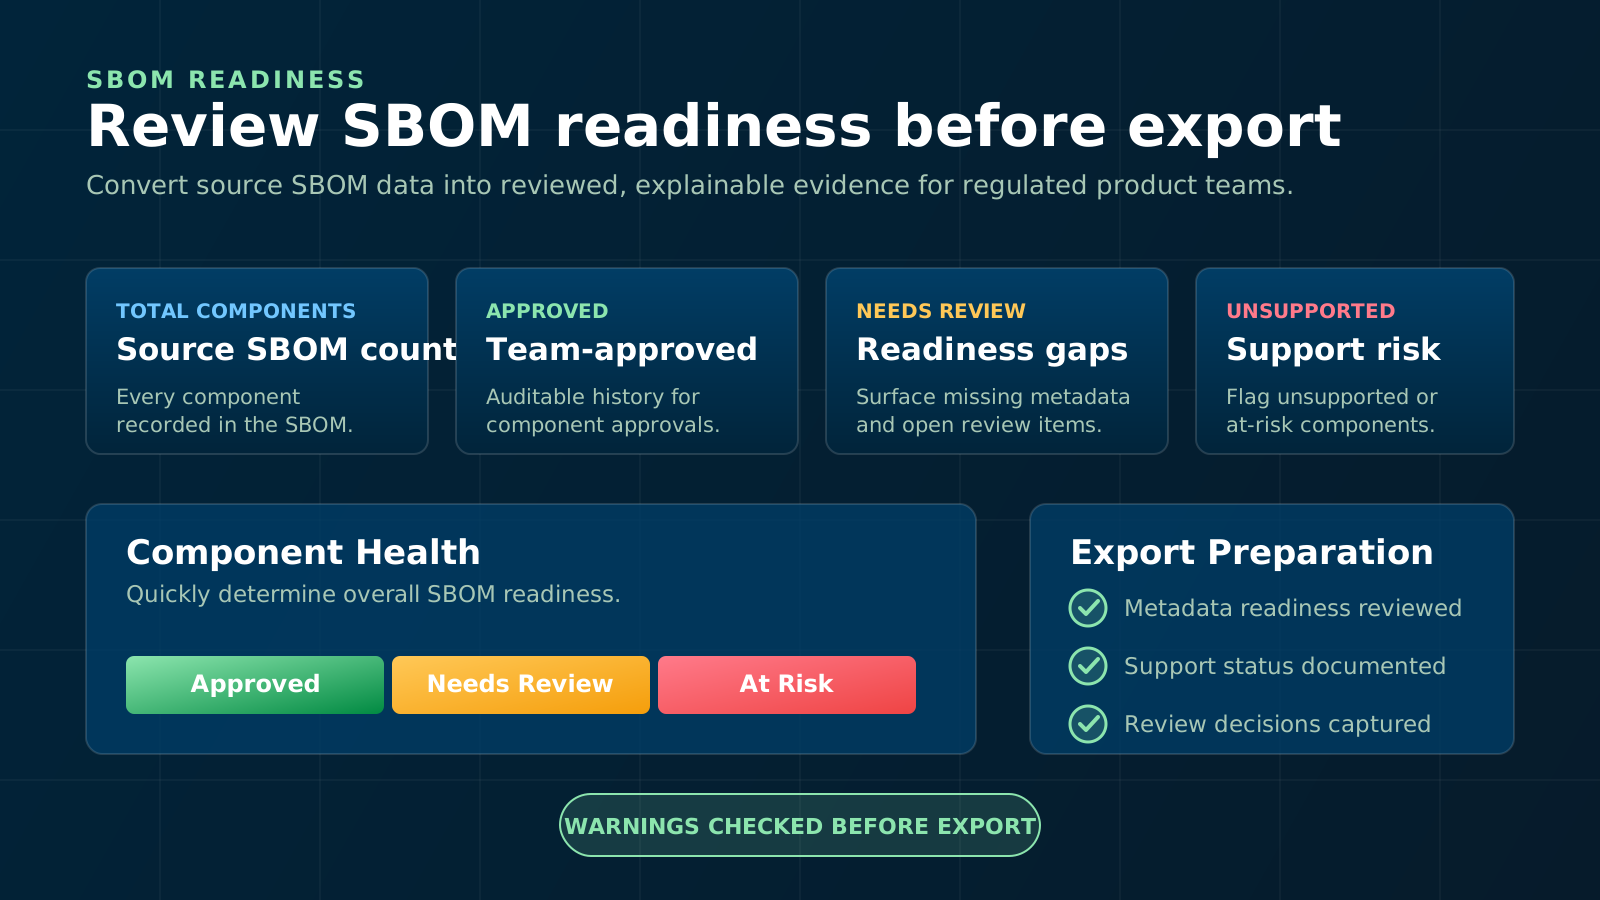
Score SBOMs against NTIA minimum elements and FDA fields, approve or exclude components, track support status and known vulnerabilities, and review supplier SBOMs alongside your own.
Produce FDA-submission-focused reports
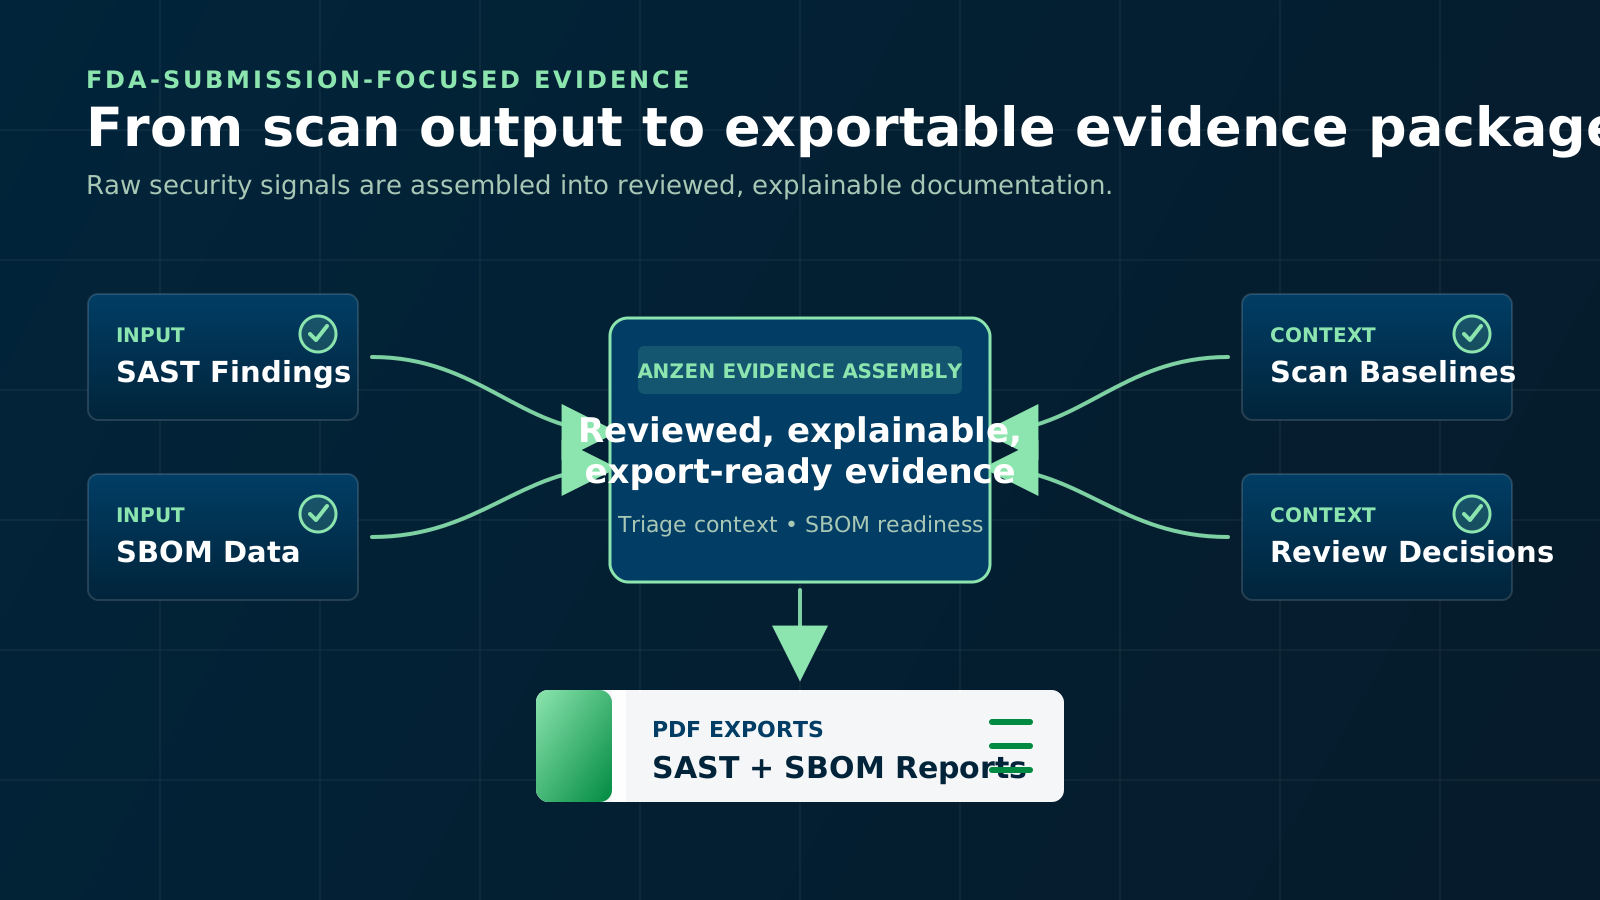
Download SAST PDF reports per scan or per project, and export SBOMs as CycloneDX (1.5–1.7), SPDX 2.3, or PDF, with missing minimum elements flagged before export.
From scanner output to submission-focused evidence.
Anzen turns raw scanner output, SBOM files, and CI results into structured outcomes your team can review, gate builds on, and export for submission work.
-
Step 1
Run scanner
Run the Anzen scanner in a local workspace or CI pipeline to collect SAST and SBOM data.
SAST + SBOM data -
Step 2
Upload results
The scanner uploads findings and the SBOM with the branch, commit, and trigger it detects, marks what is new since the last comparable scan, and can fail the build on AI-confirmed findings at a severity you choose.
Scan context -
Step 3
Review evidence
Triage findings, review SBOM readiness, and record justified decisions, each logged with who made it and when.
Review decisions -
Step 4
Export reports
Produce SAST and SBOM evidence for FDA premarket submissions and internal design records.
Evidence packages